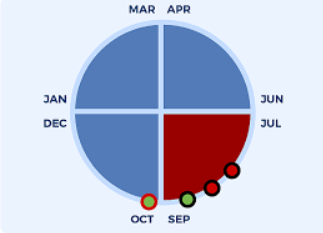
It is an external network scan, performed by Approved Scanning Vendors authorized by card schemes such as MasterCard and Visa, repeated every 3 months and required for compliance with PCI DSS rules.
The Quarterly Network Scan examines whether merchant systems are protected against external threats (such as hacking or malicious viruses). The scan must be performed by one of the Approved Scanning Vendor (ASV) companies authorized by the card schemes.
For example, details of the requirements set by Visa are given below:
Visa USA & CEMEA – Service Provider Levels and Validation Actions
| Level | Description | Validation Action |
|---|---|---|
| 1 | All VisaNet processors (members and non-members) and all payment gateways. * | 1> Annual On-Site PCI Data Security Assessment 2> Quarterly Network Scan |
| 2 | Any service provider not in Level 1 that stores, processes or transmits more than 1,000,000 Visa accounts/transactions per year. | 1> Annual On-Site PCI Data Security Assessment 2> Quarterly Network Scan |
| 3 | Any service provider not in Level 1 that stores, processes or transmits fewer than 1,000,000 Visa accounts/transactions per year. | 1> Annual PCI Self-Assessment Questionnaire 2> Quarterly Network Scan |
* According to Visa, payment gateways are a category of intermediary or service provider that stores, processes and/or transmits cardholder data as part of a payment transaction. In particular, they enable payment transactions (for example authorization or settlement) between merchants and processors (VisaNet endpoints). Merchants can send payment transactions directly to an endpoint or indirectly through a payment gateway.
Visa Asia / Pacific – Service Provider Levels and Validation Actions
| Service Providers | More than 600,000 Visa transactions per year | Between 120,000 and 600,000 Visa transactions per year | Fewer than 120,000 Visa transactions |
|---|---|---|---|
| Self-assessment questionnaire | Optional | Required | Required |
| Quarterly network scan | Required | Required | Recommended |
| On-site review | Required | Recommended | Recommended |
MasterCard – Service Provider Levels and Validation Actions
| Level | Description | Validation Action |
|---|---|---|
| 1 | All TPPs. All DSEs that store, transmit or process more than 1,000,000 total MasterCard and Maestro transactions annually. | 1> Annual On-Site PCI Data Security Assessment 2> Quarterly Network Scan |
| 2 | Includes all DSEs that store, transmit or process fewer than 1,000,000 combined MasterCard and Maestro transactions annually. | 1> Annual PCI Self-Assessment Questionnaire 2> Quarterly Network Scan |
| Merchant Level | Selection Criteria | Validation Actions | Validated By |
| 1 | Any merchant, regardless of acceptance channel, that processes more than 6,000,000 Visa transactions per year. Any merchant that has suffered an attack resulting in a compromise of account data Any merchant identified as Level 1 by any card scheme | Annual On-Site Security Audit and Quarterly Network Scan | Independent Security Assessor or Internal Audit, if signed by an officer of the company's Approved Scanning Vendor |
| 2 | 1 million to 6 million Visa or MasterCard transactions per year | Annual PCI Self-Assessment Questionnaire and Quarterly Network Scan | Merchant's Qualified Independent Scanning Firm |
| 3 | 20,000 to 1 million Visa or MasterCard e-commerce transactions per year | Annual PCI Self-Assessment Questionnaire and Quarterly Network Scan | Merchant's Qualified Independent Scanning Firm |
| 4 | All other merchants that process fewer than 20,000 Visa or MasterCard e-commerce transactions per year and up to 1 million Visa or MasterCard transactions per year | Recommended Annual PCI Self-Assessment Questionnaire and Quarterly Network Scan | Merchant's Approved Independent Scanning Firm Note: While compliance is mandatory for Level 4 merchants, validation is optional but strongly recommended |