“Software-based Mobile Payment Security Requirements” is a document published by EMVCo in April 2020 to guide payment application developers in building a secure payment application. Its Turkish title is a direct translation of the English one.
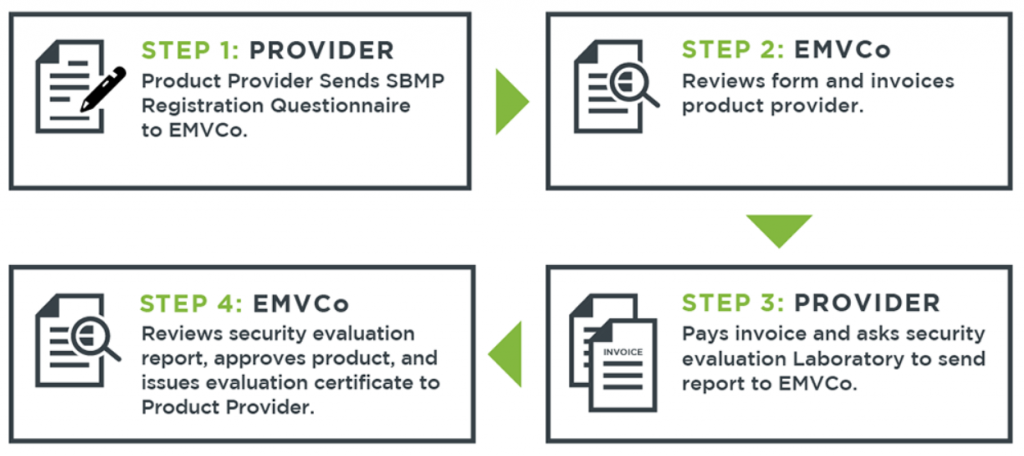
EMVCo created a Security Evaluation Process for Software-Based Mobile Payments in order to offer product providers an efficient and flexible proposition and to build a solid security foundation for SBMP (Software Based Mobile Payments) solutions. The document aims to protect payment applications, from small start-ups to the world's largest OEMs and mobile payment providers.
The document can be accessed at the link below:
Who do these requirements concern?
The document is a reference for companies that develop mobile wallet and HCE-based payment applications, for issuers, and for the test laboratories that evaluate these applications. Its aim is to bring the minimum security level into a common framework for solutions that protect card data with software rather than a hardware-based secure chip.
Typical topics include protecting the application against tampering, secure storage of keys and tokens, detection of rooted or jailbroken devices, and server-side monitoring.
For a bank, this framework acts as a checklist when performing a risk assessment for a third-party wallet or for an application it has developed itself.