Skip to content

Search

"card authorization"

241 articles found

Conceptual illustration of competing players vying for power in agentic commerce

General

Agentic Commerce Series – Part 6

Who will win in Agentic Commerce? Owning the customer used to be a huge advantage. Once an agent starts deciding on the customer's behalf, where does the real power move to?

Diagram of an Onus installment transaction flow between POS and HOST

Payment Systems

What are the key points in an Onus Installment project?

Before describing the Onus Installment process, it is better to first answer: what is an Onus transaction? An Onus transaction is when the acquirer and issuer are the same institution, so the transaction is processed through that institution.

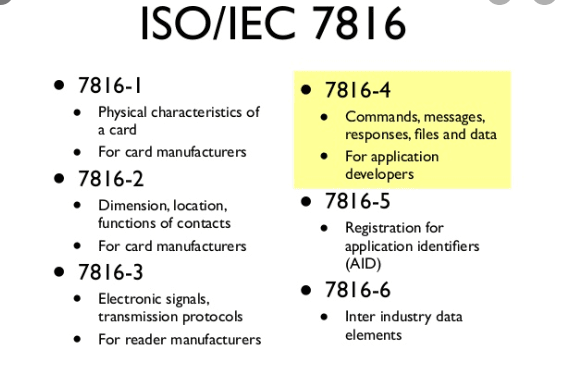
ISO/IEC 7816-5 application identifier (AID) structure

Online & Authorization

What Is ISO/IEC 7816-5?

ISO/IEC 7816-5 defines how to use an application identifier to determine whether an application is present on a card and/or to retrieve the application on the card.

Diagram explaining the MCC merchant category code field in ISO 8583 messages

ISO 8583

ISO 8583 Field Descriptions (F18)

F18-MERCHANT TYPE: This is the merchant's category code (MCC) information. It must contain values from the Mastercard or Visa MCC Code list. It is a 4-digit numeric value. For ATM transactions, MCC code 6011 should be sent. The role of MCC in authorization...

Illustration representing Strong Customer Authentication (SCA) under PSD2

Payment Systems

What is Strong Customer Authentication (SCA)?

Strong Customer Authentication (SCA) is a security requirement introduced under the EU's Payment Services Directive 2 (PSD2) to increase security and reduce fraud in online payment transactions. SCA requires two of three independent authentication factors.

GO Secure Payment logo

Merchant & POS

What Is Secure Payment (GO)?

GO Secure Payment is a system developed by BKM that verifies cardholders using a one-time password (OTP) during online purchases made with TROY cards, providing banks with a secure verification platform without needing to store card data.

Diagram showing the CAT (Cardholder Activated Terminal) Indicator field used in payment authorization messages

Merchant & POS

What is the CAT (Cardholder Activated Terminal) Indicator?

CAT (Cardholder Activated Terminal) devices are typically unattended terminals that accept various payment cards. These terminals are frequently installed at railway ticket stations, gas stations, toll roads, parking lots, and other commercial locations.

Smartphone being used as a mobile POS device for a card payment

Merchant & POS

Mobile Phones Are Turning Into POS Devices

With advances in technology, mobile phones can now be used for many functions besides calls and internet access. One such innovation is the ability to use smartphones or tablets as POS devices.

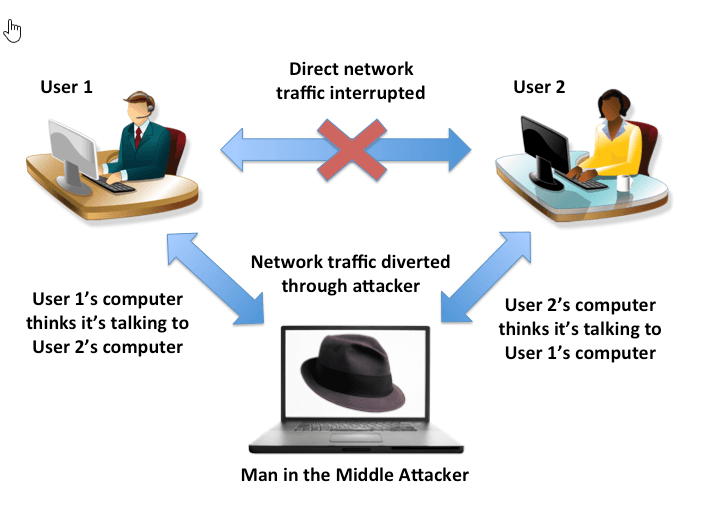
Diagram illustrating a man-in-the-middle attack intercepting communication between a client and a server

Fraud

What is a Man-in-the-Middle Attack (MITM)?

A man-in-the-middle attack is a method in which an attacker inserts themselves between the server and client to intercept users' information, steal passwords, and gain access to accounts on a local network. This fraud mostly occurs over public internet connections.