Chargeback
What are the chargeback dispute types?
A chargeback is a dispute raised against a card transaction when the cardholder did not make it or does not recall it. The dispute types vary depending on the situation; let's look at them.
Search
116 articles found
Chargeback
A chargeback is a dispute raised against a card transaction when the cardholder did not make it or does not recall it. The dispute types vary depending on the situation; let's look at them.
Fraud
Fraud management is used to detect possible fraud on customer accounts and provides additional security for transactions when necessary, making it one of the top priorities for banks.
HCE
The HCE cloud-based security infrastructure consists of four main pillars: Tokenization, Risk Management, Session Keys, and User/Device Authentication. Tokenization indicates the type of token generation, and there are three different tokenization methods.

ISO 8583
F18-MERCHANT TYPE: This is the merchant's category code (MCC) information. It must contain values from the Mastercard or Visa MCC Code list. It is a 4-digit numeric value. For ATM transactions, MCC code 6011 should be sent. The role of MCC in authorization...
HCE
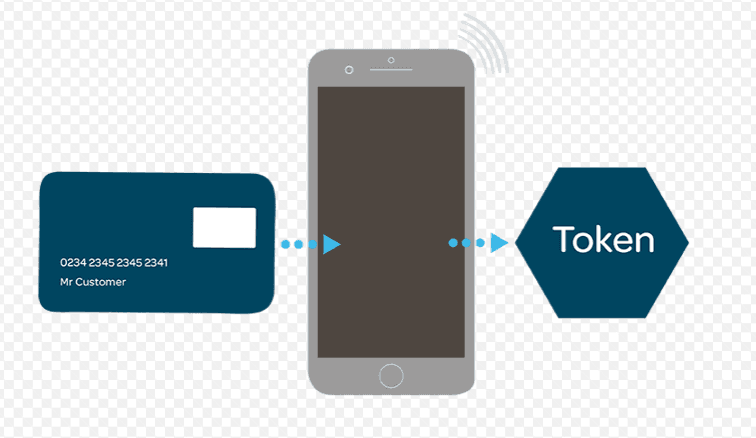
Token types vary depending on the verification method used in a transaction. In offline transactions, general checks are performed by the mobile app and card reader without any verification in the card system. In online transactions, token verification is sent to and verified by the issuer.

Merchant & POS
In the first post I explained what closed-loop payment systems are and how they differ from open-loop ones. Many of the replies I received boiled down to one question: how do these systems actually work behind the scenes once a QR code is scanned?
Fraud
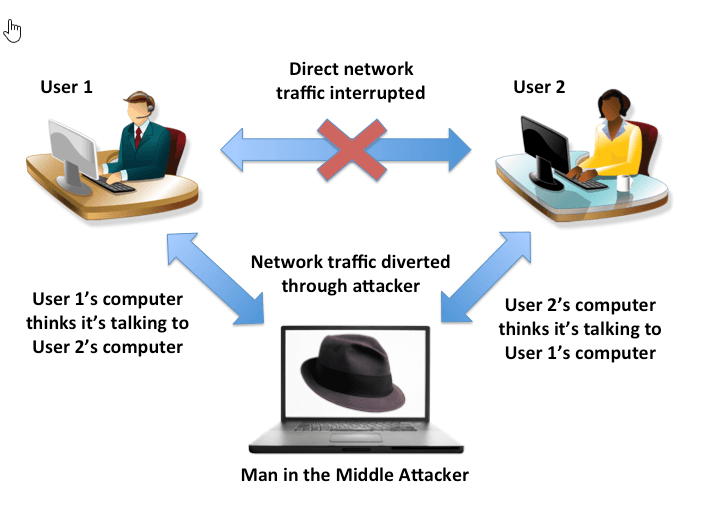
A man-in-the-middle attack is a method in which an attacker inserts themselves between the server and client to intercept users' information, steal passwords, and gain access to accounts on a local network. This fraud mostly occurs over public internet connections.

Payment Systems
Offline transaction parameters are divided into two types: contact offline and contactless offline. These parameters can be managed separately through Terminal data and Chip data. Offline transactions can be reported to the HOST after an online transaction, after X occurrences, and more.
Payment Systems
According to the Banks Association of Turkey, collusive transactions that misuse POS devices, debit cards, or credit cards for purposes other than their intended use are called fictitious transactions - in short, transactions used outside their intended purpose.
Payment Systems
A non-secure transaction is an e-commerce transaction approved without any verification before authorization, such as SMS OTP. In short, authorization is obtained by verifying only the card number, expiration date, and CVV2.
ATM
Because the ATM is the channel where customers physically handle cash, fraud cases happen there very often. Here are the precautions you can take to use ATMs safely.
Security
These are passwords generated for one-time use and sent to the cardholder's phone to verify card transactions in payment systems. The password sent during a 3D Secure transaction is a common example.