Skip to content

Search

"HCE"

15 articles found

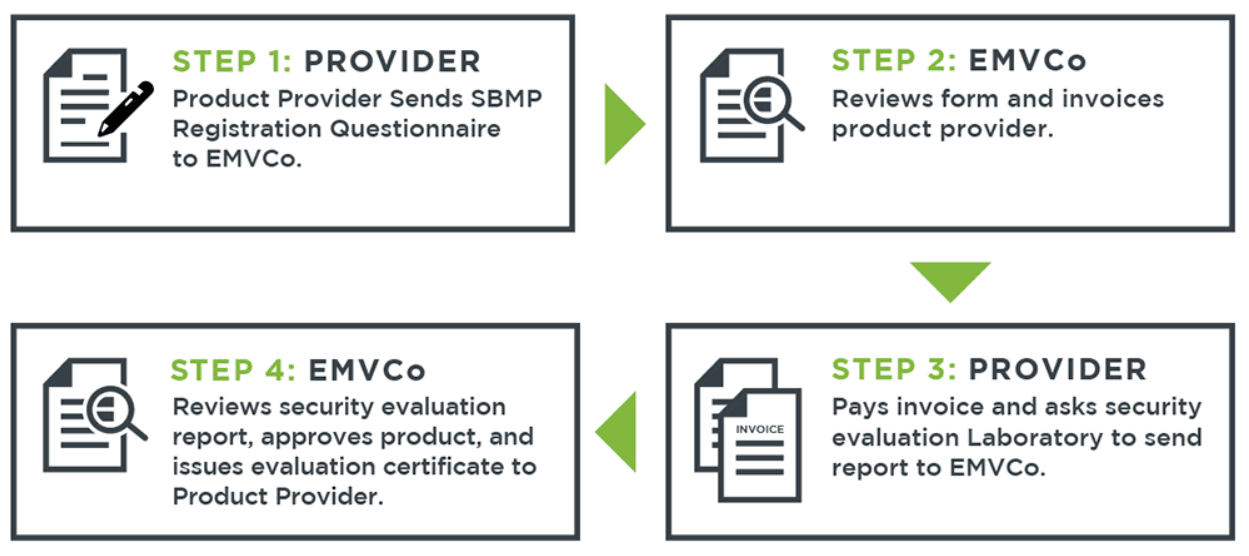
Cover of the EMVCo Software-based Mobile Payment Security Requirements document

Security

What is Software-based Mobile Payment Security Requirements?

“Software-based Mobile Payment Security Requirements” is a document published by EMVCo in April 2020 to guide payment application developers in building secure payment applications. This post summarizes its purpose and who it concerns.
Physical credit card compared with a virtual card on a mobile phone

Credit Card

Physical or Virtual Credit Card: Which Do You Prefer?

Digitalization is reshaping payment systems. Credit cards are moving from physical plastic to virtual cards, e-wallets and mobile payments. Will physical card use disappear completely? Here is a look at the trends, Generation Z and the remaining gaps.

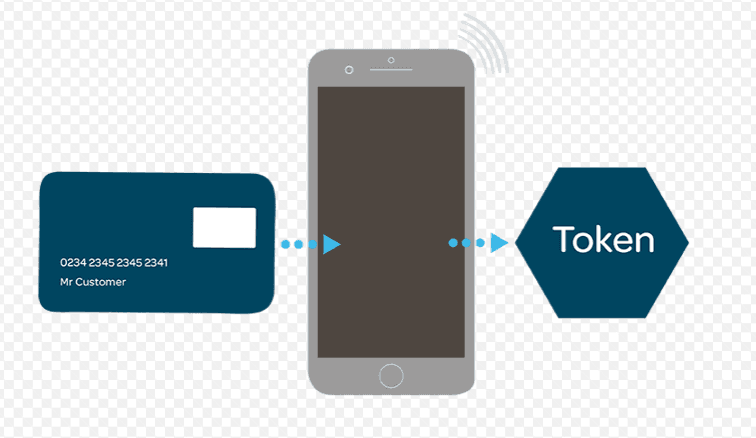
Diagram comparing the three levels of payment-card tokenization: static, semi-dynamic and dynamic

HCE

What Are the Levels of Tokenization?

Generating a token from the card number is essential to the security of payments made with mobile devices. The level of tokenization used depends on the need and on how critical the token is. Static tokenization: the token is generated once and stored in a database.