Skip to content

Search

"fraud risk"

58 articles found

Comparison of online and offline token verification in payment transactions

HCE

What Are Transaction-Based (Online/Offline) Token Types?

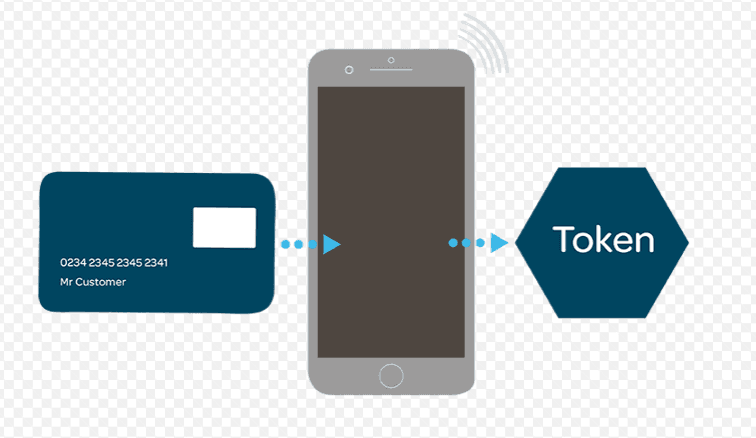
Token types vary depending on the verification method used in a transaction. In offline transactions, general checks are performed by the mobile app and card reader without any verification in the card system. In online transactions, token verification is sent to and verified by the issuer.

Illustration representing real-time and near real-time fraud monitoring in payment systems

Fraud

What is Online (Real Time) and Near Online (Near Real Time) Fraud?

Fraud monitoring refers to tracking card transactions through scenarios to detect potential fraud and taking rapid action immediately before or after a transaction occurs - such as identifying a suspicious transaction, calling the customer, or temporarily blocking the card to prevent authorization.

Application fraud and transaction fraud controls

Fraud

What Are the Types of Fraud Controls?

Fraud controls fall into two main types: application fraud controls, which check card and merchant applications, and transaction fraud controls, which monitor card and POS transactions.

FAST instant payment transaction limit

FAST

What Is the FAST Transaction Limit?

The limit in FAST, the CBRT's new instant payment system launched on 8 January, started at 50 TL. It was raised to 250 TL on 14 January and 500 TL on 21 January, and will be raised to 1,000 TL on 28 January.

Diagram showing the four pillars of HCE cloud-based security infrastructure

HCE

What is the HCE Cloud-Based Security Infrastructure Like?

The HCE cloud-based security infrastructure consists of four main pillars: Tokenization, Risk Management, Session Keys, and User/Device Authentication. Tokenization indicates the type of token generation, and there are three different tokenization methods.

Diagram illustrating card fraud and forgery in card payments

Security

What Is Forgery in Card Payments?

Forgery in card payments means transactions made with card details without the cardholder's knowledge, or purchases with counterfeit or stolen cards. Merchants cannot eliminate fraud and chargeback risk, but they should aim to reduce it to reasonable levels.

Illustration of customer-based contactless card limit management

Payment Systems

Can a Card's Contactless Limit Be Managed on a Per-Customer Basis?

Contactless payment has greatly improved the user experience, yet its fixed transaction limit is a common complaint. Can this limit be managed dynamically per customer? This post covers the current situation, technical and regulatory requirements and the outlook.

Architecture diagram of the Visa EAS Server within the Visa Secure 3-D Secure authentication flow

EMV

What Is the Visa EAS Server?

The Visa EAS Server (Extended Access Service) is a server used in Visa’s authentication infrastructure. It was developed to run the cardholder authentication process securely between banks and the Visa network, particularly within Visa Secure (3-D Secure 2.x).

Diagram illustrating the appeal stage of the card dispute and chargeback process between issuer, acquirer and card scheme

Payment Systems

What Is an Appeal? What Does It Mean in Payment Systems?

In payment systems, an “appeal” is the process of objecting to the outcome of a transaction dispute. It is usually discussed alongside chargebacks, but it plays a critical role in interbank dispute resolution, when a party asks the card scheme to re-evaluate a concluded decision.