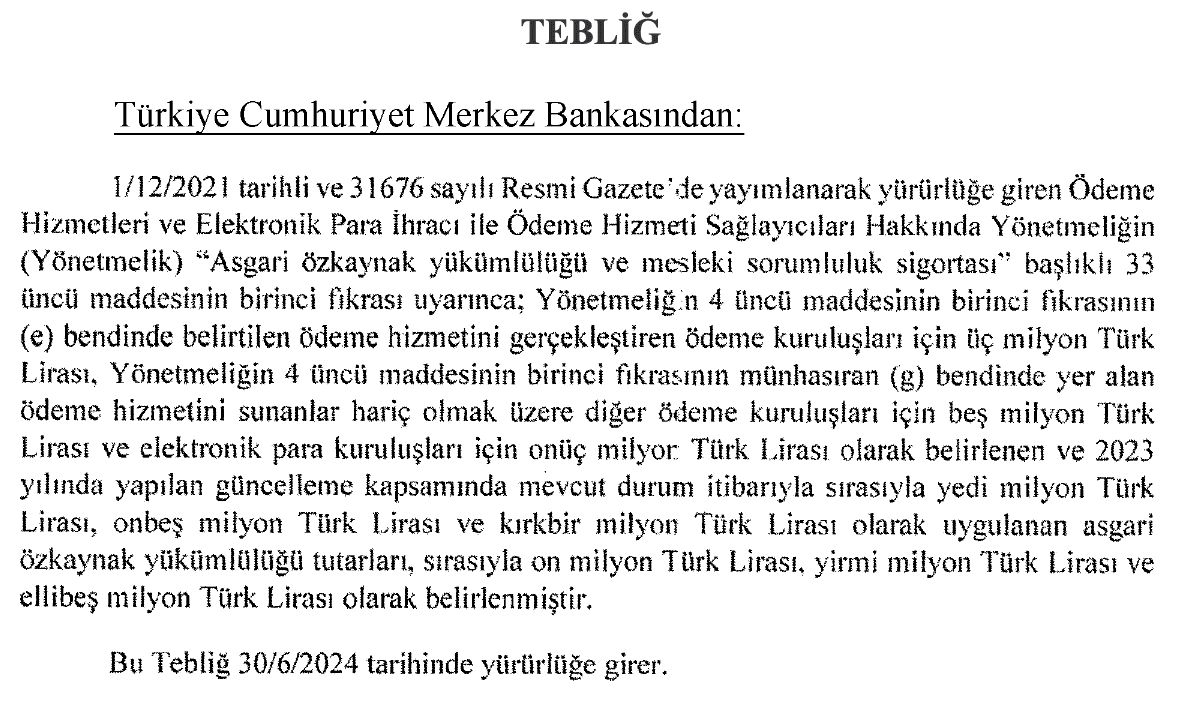
An amendment was made on 7 October to the Communiqué on Information Systems of Payment and Electronic Money Institutions and Data Sharing Services of Payment Service Providers in the Field of Payment Services, which was first published on 1 December 2021.
You can access the Communiqué dated 7 October at the link below:
https://www.resmigazete.gov.tr/eskiler/2023/10/20231007-12.htm
A detailed comparison of the Communiqué dated 1 December 2021 and the Communiqué dated 7 October is given in the document at the link below on the TODEB website. I am leaving the link below:
https://todeb.org.tr/source/duyurular/2023_10/TODEB_07102023_Teblig_Degisiklik_Tablosu.pdf
In addition to the information above, I am including below the article shared on this topic at fintechistanbul.org:
The Central Bank of the Republic of Turkey (“CBRT”) published an Amendment Regulation* and Communiqué** (the “Amendment Rules”) containing critical changes and innovations to the following two pieces of secondary legislation known in the fintech field. They entered into force with their publication in the Official Gazette dated 7 October 2023. Regulation on Payment Services and Electronic Money Issuance and Payment Service Providers (the “Regulation”) Communiqué on Information Systems of Payment and Electronic Money Institutions and Data Sharing Services of Payment Service Providers in the Field of Payment Services (the “Information Systems Communiqué”) Considering the changes and new additions made by the CBRT, it appears that the new rules affect not only licensed fintechs but also companies operating without a license under the technical service exemption, outsourcing service providers, and even, indirectly, card scheme operators. Because certain business models on the card storage and wallet side are now brought within the scope of licensing, it will be important for companies with these products to assess their position correctly and carry out the necessary licensing processes. The major innovations and changes introduced by the Amendment Rules can be summarized under the following main headings. The Digital Wallet Business Model Has Been Defined and Made Subject to a License With the CBRT's new rules, the “Digital Wallet” has been defined for the first time in Turkish legislation, and the rule has been introduced that this service, apart from the stated exceptions, may only be offered by payment service providers (that is, payment and/or e-money institutions, banks, or PTT). Therefore, the main rule is that companies offering a digital wallet service within the scope of the definition must obtain a license. In this context, the CBRT's definition of a digital wallet is as follows. “A payment instrument offered as an electronic device, online service or application in which information on the payment account or payment instrument defined by the customer is stored, and which enables the customer to carry out payment transactions using the information on the payment account or payment instrument that the customer has defined” At this point, the CBRT has also stipulated that “electronic devices, online services or applications in which only the payment account held with the payment service provider offering the service and the payment instrument issued by that payment service provider can be defined and stored” will not be considered a digital wallet service. Given the breadth of this definition, it is assessed that it covers not only digital wallets that hold funds (e.g. a Staged Wallet) but also digital wallets (Pass-Through Wallets) that merely serve a card storage function through tokenization, which until now relied on the technical service provider exemption. The CBRT requires institutions offering a digital wallet service within the scope of this definition to hold a license, at a minimum, limited to “issuance of payment instruments”, and, if the scope of the service offered to the customer requires it, a license for other payment services as well. With the new rules, it has also been stipulated that these institutions must hold e-money where the digital wallet is used as a payment instrument at merchants and the funds for the payment transaction are transferred through the institution offering the digital wallet service (e.g. a Staged Wallet), and must hold a Payment Initiation Service license where, in a payment transaction made at merchants, the payment account held with another payment service provider or the payment instrument issued by another payment service provider that has been defined in the digital wallet is used directly (e.g. a Pass-through Wallet). Considering the state of the sector, it is known that the Staged Wallet type of business model is run by institutions holding an e-money license. However, the CBRT's critical and noteworthy rule concerns the model known in the sector as the Pass-Through Wallet, which works through the tokenization of an existing payment instrument and does not hold funds. The CBRT has treated the service offered by the institution providing the wallet in this business model as a payment initiation service, which is an open banking service. This interpretation, which clearly differs from the Payment Services Regulation 3 whose draft was recently published by the EU and which is expected to replace PSD2, is, as far as we know, the first example that combines the open banking business model with card-based transactions. At this point, what already-licensed players need to watch is to carry out the necessary legal assessments and decide whether they need to apply for a license extension for the payment initiation service and other required services. With the new rules, the digital wallet has been defined and this service has been designated as a licensed service, but the exceptions to it have also been defined. In this context, it has been stipulated that, in applying the article on the digital wallet service, the payment service exceptions in the second paragraph of Article 12 of Law No. 6493, the closed-loop e-money provisions in the fifth paragraph of Article 18, and the provisions on prepaid instruments that can only be used within a specific service network are reserved. Because of this provision, we assess that wallets known in the sector as “closed-loop” are not subject to the newly introduced obligations. In addition, the Amendment Rules stipulate that card storage business models meeting certain conditions are also within the scope of the exception. In this regard, it has been stipulated that services will not be considered a digital wallet service under the Regulation where they store sensitive customer data on behalf of the merchant or payment service provider within the limits permitted by the legislation, where the legal entity doing the storing is in no way a direct party to any legal transaction with the customer, where it does not create the impression for the customer that the payment transaction is carried out through the legal entity doing the storing, where the legal entity doing the storing is at no point in the payment transaction the owner of the funds subject to the payment transaction, and where the rights and obligations relating to the activity carried out are clearly set out in the contract between the parties. Within the scope of the Technical Service Provider Exemption, the service of institutions that provide card storage technical support to merchants or payment service providers within the relevant scope, so to speak behind the scenes, has been left outside the scope of the digital wallet. These institutions do not need to obtain a license. With the new rules, it has also been stipulated that, under the Technical Service Provider Exemption, persons who store sensitive customer data on behalf of the merchant or payment service provider within the limits permitted by the legislation cannot be the sole visible face of this service toward the customer. Finally, it should be noted that, with the Amendment Rules, the deadline for obtaining the necessary licenses for services falling within the scope of the digital wallet is 7 October 2024. The Activities That Institutions May Carry Out Have Been Expanded As is known, activities of institutions other than payment and e-money are subject to a quite strict regime under the legislation. With the amendment, the following have been added to the activities that payment and e-money institutions may offer, in addition to the activities already permitted. Interface providership (excluding, directly or indirectly, transactions related to the trading of precious metals and precious stones and foreign exchange) Leading service, that is, ancillary services that may increase the use of the institution's payment services, such as marketing offered to the customer and referral to the systems of the relevant financial institution so that the customer can reach the services of financial institutions whose activities are regulated and supervised by an authorized authority under the relevant legislation (excluding transactions related to foreign exchange trading) Intermediation in activities related to the trading of precious metals and precious stones (provided that the transaction amount the institution will intermediate in a month is limited to a maximum of one percent of the payment volume in the previous calendar year) Qualified Services and Value-Added Services (limited to the scope defined in the Legislation) The CBRT has also explicitly stipulated, in terms of the legislation, that institutions holding an open banking license may offer information services on other accounts held with payment service providers that are not considered payment accounts. It should be noted that certain limitations have also been introduced on carrying out the services mentioned above. In this context, the CBRT has stipulated that the services offered by institutions under the leading service cannot cover the entirety of the core activity of the financial institution to which the service is provided and that, while providing the services, they cannot assume any function other than the matters regulated in the legislation; that institutions cannot themselves directly trade in precious metals and precious stones; that the maximum amount each customer may hold in their balance within a calendar year under precious metals and precious stones trading intermediation activities cannot exceed one thousandth of the amount determined as one percent of the institution's payment volume in the previous calendar year; and that institutions holding an open banking license may offer value-added services and qualified services in relation to accounts held with other payment service providers in addition to accounts held with themselves, whereas other institutions may offer these services only in relation to the accounts held with themselves. Considering the changes above, we see that the very limited fields of activity of fintechs have been expanded in line with the requirements of the age and in a way that yields results in favor of consumers, and we think this is positive. However, it should also be noted that there has been no development on microcredit, which fintechs have long been waiting for. At this point, it should be underlined that building the right contractual structures and UX/UI designs when offering the relevant services to customers is critical for compliance with the legislation. Otherwise, stepping outside the limits of the permitted activities may lead to sanctions. An Equal Treatment Rule Toward Other PSPs Has Been Introduced for PSPs with a Control Relationship Between Them (e.g. a Bank and Its Subsidiary Holding a Payment License) Where a PSP offers infrastructure services relating to the payment account services and payment services it provides (e.g. POS) to other PSPs, including a PSP that it controls, it is now obliged to offer the same kind of services to the PSP it controls and to the other PSPs under the same terms and conditions and with the same fee policy, and not to steer or force its own customers to receive services from the PSPs it controls in a way that would put the PSP it controls in an advantageous position over other PSPs. In addition, except in cases of interface providership, PSPs controlled by another PSP are obliged not to use, in any document, notice, advertisement or public statement relating to the services they will offer, expressions that give the impression that they are acting on behalf of the PSP that controls them. In applying the rules above, obligations arising from the Legislation and practices to the contrary that may arise due to security, operational and technical requirements are reserved. It is assessed that this provision will affect cases where banks with payment or e-money institution subsidiaries provide those subsidiaries with POS, payment account access or other infrastructure. Equal Treatment and Honour All Cards Obligations Regarding Payment Instruments (Cards) Have Been Introduced With the new rules, where payment service providers that issue payment instruments (e.g. cards) issue payment instruments compatible with more than one card scheme operator and the customer requests that the payment instrument be issued as defined for a specific card scheme operator, they are obliged to issue the payment instrument compatible with the card scheme operator the customer wants. In addition to this obligation, the rule has been introduced that, before and after the issuance of the payment instrument, these institutions must not apply different practices to the customer depending on the card scheme operator in a way that would make the process of issuing a payment instrument compatible with the customer's chosen card scheme operator harder for the customer. On the other hand, payment service providers that accept card-based payment instruments are obliged to ensure that the devices, hardware and software they use in their acceptance activities are compatible with the card schemes established by systemically important payment system operators authorized to carry out card scheme operator activities, and that payment instruments issued compatibly with these infrastructures can be used at the merchants they serve. In addition to this obligation, under the honour all cards principle, payment service providers have been obliged to give merchants the necessary support for the compliance work mentioned above, and the CBRT has been authorized to require a payment service provider to suspend the payment infrastructure services it provides to a merchant that makes no effort to take the necessary measures within the scope of this compliance work without providing a reasonable justification. Considering that the systemically important payment system operator in our country is Interbank Card Center (“BKM”) and that the card scheme established by BKM is TROY, it is assessed that the phrase “compatible with the card schemes established by systemically important payment system operators authorized to carry out card scheme operator activities” in the relevant rule refers to TROY. The Way Has Been Opened for Open Banking Companies to Offer Qualified Services to Individuals As is known, one of the innovations introduced by the secondary legislation was the definition of “value-added service”. The CBRT defined “services that make the administrative and operational processes of legal entities and merchants easier, more secure or more effective” as value-added services and stipulated that open banking institutions offering these value-added services would not be subject to the activity prohibition. With the new rules, the CBRT has determined services of this nature for individuals as well, in parallel with the definition of value-added service, and defined them as “qualified services”. In this context, the following services have been defined as “Qualified Services”. “Services that do not fall within the scope of payment services under the Law but that make payment services easier, more secure or more effective by supporting the financial situation and financial awareness of individuals, such as personal budget management, bill management, account verification and payment reminders” In this context, the way has been opened for open banking companies to offer “qualified services” not only to legal entities but also to individuals without running into the activity limit. The Collateral Amount Has Been Set as a Deduction Item in the Calculation of Equity Before the new rules, under the legislation, the collateral amount held by institutions was not included in the equity calculation. With the amendment, the provision has been introduced that the relevant collateral amount will be treated as a deduction item in the equity calculation. In addition, the requirement that “the free reserves included in the equity calculation must be available to the institution at all times to cover losses that may arise from risks, must be clearly shown in the accounting records, and must be approved by the independent audit firm carrying out the institution's independent audit” has been removed. On the other hand, it has been explicitly stated that the regular and continuous reporting made to the CBRT will not replace the notification that the institution must make to the CBRT if equity falls below the minimum limit set for the institution. Finally, an explicit rule has been introduced that payment and e-money funds cannot be shown as collateral. The Rules for Calculating the Collateral Amount Institutions Hold with the CBRT Have Been Relaxed Many of the existing criteria in determining the total collateral amount that institutions must hold with the CBRT have been removed, and by determining that the criteria for determining the collateral amount are only the following, it has been stipulated that the collateral amount will be increased by twenty-five percent if these criteria are not met individually and by one hundred percent if they are not met together. No administrative fine has been imposed under the Law. The share of complaints and objections concluded against the institution before the Association arbitration committees under Article 74 in the total applications concerning the institution must not exceed ten percent. Limiting Time Periods Have Been Introduced for Licensing Processes With the new rules, regarding the licensing process, it has been decided that the license application will be deemed not to have been made if deficiencies in the information and documents at the initial notification stage are not remedied within three months from the notification of the CBRT letter on the deficiency; that, in the license extension process, the activity extension application with the CBRT will be deemed not to have been made if deficiencies in the information and documents are not remedied within six months from the date of notification of the CBRT letter on the deficiency; that independent audit firms that may issue the report to be obtained on matters not directly related to information systems must be on the list of Independent Audit Firms authorized to conduct independent audits, “including for public interest entities”; and that the Findeks credit score and the Bankruptcy Concordat document are to be requested for the natural/legal person qualified shareholders of the applicant company and for the persons who hold control. Share Acquisitions and Transfers Between Companies in the Same Group Have Been Removed from the Scope of CBRT Permission Under Certain Conditions With the new rules, “share acquisitions and transfers between companies belonging to the same group that do not cause any change in the direct or indirect shareholding of the institution's ultimate shareholders in the institution” are no longer subject to the CBRT's permission, and notifying the CBRT of share acquisitions and transfers of this nature is sufficient. However, it is important to note that, even if such a transaction is subject to notification, the CBRT reserves the right to require the transaction to be reversed. For this reason, the agenda relating to the relevant processes must be set out carefully. A Duty of Care Regarding Localization Has Been Introduced for Outsourcing Critical Information Systems It has been stipulated that maximum care must be taken so that the products and services procured within the scope of critical information systems and security are produced in Turkey or their manufacturers' R&D centers are located in Turkey, and that this must be treated as an important criterion in outsourcing. At the same time, the requirement has been introduced that such providers and manufacturers have incident response teams in Turkey. Processes to Be Carried Out via a Remote Communication Tool Are Being Detailed Various rules have been introduced on the technology and methods to be used for identity verification and for establishing the contractual relationship to be carried out via a remote communication tool, and these systems have been brought within the scope of critical information systems. At the same time, it has been stipulated that the process in Article 22, paragraph 1 of the Regulation may be left unapplied in “operating the processes for the necessary information, contracts, receipts and similar documents for legal entities offering virtual terminal services under the third paragraph of Article 2.2.11 of the Financial Crimes Investigation Board General Communiqué (Serial No: 5)”. A “MASAK Monetary Limit” Has Been Added to the Definition of “Anonymous Prepaid Instrument” The definition of anonymous prepaid instrument in the Regulation has been supplemented so that one of the conditions for being a prepaid instrument is “remaining below the monetary limits in MASAK Serial No: 5”. The Way Is Being Opened for the Institution's Subsidiaries That Provide Information-Systems-Related Services to Its Affiliates to Provide Group Cloud Services Under the existing Regulation, the rule for group cloud service as an outsourced service is that it be “provided by a credit institution or financial institution that is the institution's parent, affiliate or an affiliate of its parent, and whose activities relating to information systems are regulated and supervised by an authorized authority under the relevant legislation”. With the amendment, the way is being opened for “subsidiaries that provide information-systems-related services to the actors listed above” to also provide this service (group cloud service) to the institution. Data Transfer Abroad Has Been Relaxed With the addition to the Regulation, where one of the parties to the payment transaction (itself or its service provider) is located abroad, an institution is permitted to share the data needed with the relevant third parties abroad, on the condition that the data continue to be stored in Turkey, limited to what is required for the payment transaction to be carried out smoothly, in accordance with the principle of proportionality, depending on a request or instruction from the customer, and without prejudice to the obligations under Article 9 of the Personal Data Protection Law No. 6698. On the other hand, the CBRT has been given the authority to prohibit the sharing or transfer of any data with or to third parties abroad, or to impose additional restrictions on them, if it decides as a result of its assessment that this would adversely affect the development of the payments field. The Obligation to Encrypt Competition-Sensitive Data Has Been Removed Under Article 9, paragraph 3 of the Communiqué, “sensitive customer data and customer information and competition-sensitive data are essentially to be stored in encrypted form or in secure components”. With the amendment, “competition-sensitive data” has been deleted from the text of the provision, and encryption of this data has gone from an obligation to a preference. Additions Have Been Made to the Audit Trail Details, and What to Do if the Logging System Stops Has Been Relaxed The rule has been introduced that institutions must keep, as an audit trail, “the communication network protocol, time, and source and destination port and IP information” in addition to the information on the application through which access or the transaction took place. In addition, the rule that “if the audit trail logging system stops for any reason, no transaction is allowed to take place until the audit trail logging system is brought back into service” is being relaxed, and the scenarios to be applied and the responsibilities if logging stops are being determined. The Upper Limit Amounts for Mobile Payments Have Been Updated The upper limits of five hundred TL for the transaction limit and one thousand two hundred fifty TL for total spending set for mobile payments have been updated to “one thousand TL” and “two thousand seven hundred fifty TL” respectively; and it has been stipulated that payments for queries made through the Traffic Insurance Information and Monitoring Center, and payments for aid and donation purposes, will not be taken into account in calculating these limits. In addition, for mobile payments, the “fifteen”-day period counted from the bill's due date has been revised to “thirty days”. Rules on the Use of Merchant Information Have Been Introduced Among the cases in which the merchant information that institutions share with acquirer institutions for the PF infrastructure they use when serving merchants may be used, the processes of putting into service the infrastructure used at the merchants to which the payment service provider using the infrastructure will provide payment services, and of making the necessary technical definitions with the payment service provider whose infrastructure is used, have been added. Minor Amendments Have Been Made to Agency Processes With the additions and changes made to the agency provisions: TODEB has been required to keep a separate list of persons with whom institutions have terminated the agency relationship; the information stated in the agency list maintained at TODEB has been revised; in agency relationships between two institutions, the rule has been introduced that the information of both institutions must be included in the information provided to customers, and it has been stipulated that the institution acting as agent is responsible for implementing the information requirements at the places of work. Title Changes Have Been Removed from the Approval Requirement and Made Subject to Notification Title changes made by an institution were previously subject to CBRT approval; with the amendment, it has been stipulated that title changes must be notified to the Bank within twenty business days after the institution's internal processes for the change are completed. A Rule Requiring Risk Management Personnel to Be Full-Time Employees of the Institution Has Been Introduced It has been made mandatory that at least one of the risk management personnel within the institution be a full-time employee of the institution. Rules on Precautionary Measures, Seizure and Similar Administrative and Judicial Requests Concerning Payment and E-Money Funds Have Been Added With the new rules, it has been stipulated that all kinds of administrative and judicial requests such as precautionary measures and seizure concerning payment service users' rights and receivables held with the institution are to be fulfilled exclusively by the institution; and that requests received by the banks where the safeguarding account is held are to be fulfilled by the bank, limited to the relevant funds, if the bank has information on the ultimate ownership of payment or e-money funds on a per-customer basis of the institution, and that the bank must inform the relevant institution without delay. The Rule of Tracking Funds Collected in Exchange for E-Money on a Per-Customer Basis Has Been Introduced E-money institutions are required to keep records of the funds they receive in exchange for e-money issuance in such a way that the funds can be tracked on a per-customer basis, excluding those relating to anonymous prepaid instruments. The Time Periods Under the “Payments Made to a Payment Account” Provision Have Been Extended for Non-Consumer Customers The provision that non-consumer customers may determine a period different from the periods in the first paragraph of Article 67 with respect to payments made to a payment account has been made applicable to the whole of that article. The Amounts Relating to Low-Value Payment Transactions and Payment Instruments Have Been Updated The amounts of three hundred TL, which is the determining upper limit for low-value payment transactions and payment instruments, have been updated to one thousand TL, and the amounts of five hundred TL have been updated to two thousand two hundred fifty TL. The Compliance Periods Relating to Open Banking Have Been Extended With the new rules, on the open banking side, it has been stipulated that payment service providers that do not give their customers direct online access to the payment accounts held with them may fulfill their obligations relating to BKM integration until 31/12/2025; that payment service providers holding payment accounts may provide, until 30/6/2024, to those whose licensing process is ongoing and to institutions that have obtained an open banking license, services using non-standard services other than BKM GECIT; that open banking institutions whose licensing process is ongoing may provide the data sharing services in BKM GECIT until 30/6/2024 using non-standard services; and that banks and open banking institutions may provide, until 30/6/2024, the data sharing services determined by BKM GECIT using non-standard services with respect to payment accounts held with payment service providers that were not among the top ten participants by total number of payment-to-account transactions carried out in Bank Payment Systems during 2020.