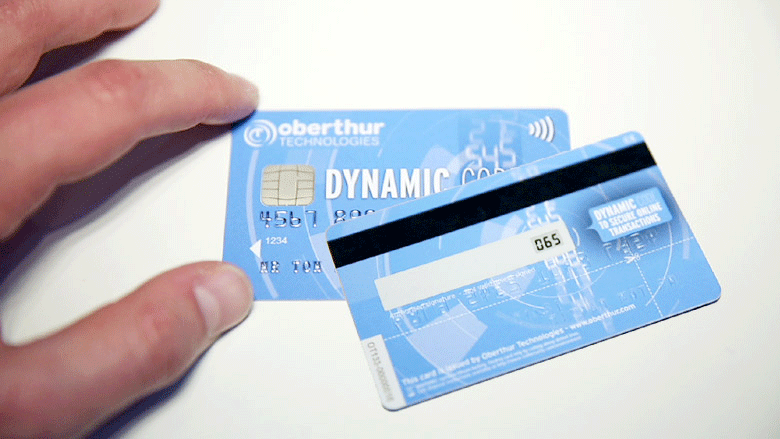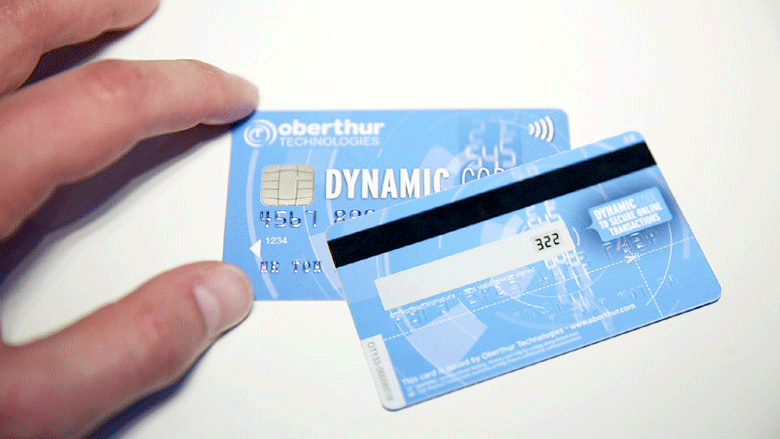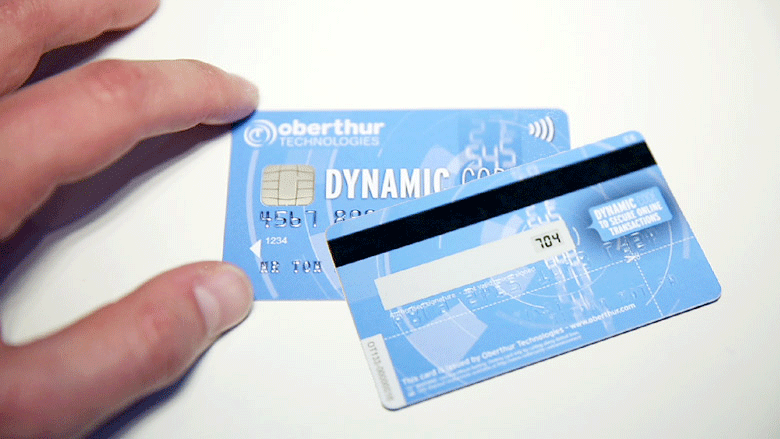
It is a CVV2/CVC2 code that changes every x minutes, depending on the issuer's design, instead of the CVV2 or CVC2 code printed on the back of a credit card.
The purpose of the dynamic CSC code is to reduce potential fraud risks in CNP (Card Not Present) transactions.
How does it work?
The dynamic security code can be offered in two different ways:
- Cards with a display: The security code is shown on a small electronic display on the back of the card, and the code changes at set intervals. The card contains a battery and a chip that generates the code.
- Mobile app: The security code does not appear on the card. The cardholder views the code through the bank's mobile app. The code changes after a set period or with each use.
How does the issuing bank verify the code?
Since the bank knows the algorithm used to generate the code and the card's key, it can calculate which code should be valid at the moment of the transaction. If the code received does not match the code that is valid at that moment, the transaction is declined.
Benefit
A static security code can be used indefinitely once card details are compromised. With a dynamic code, however, a compromised code becomes invalid shortly afterward. This makes it harder to make online purchases with stolen card details, even if those details are exposed in a data breach.
Disadvantages
Cards with a display are costly to manufacture, and battery life can limit how long the card remains usable. With the mobile app method, the cardholder has to open the app for every online purchase. How the dynamic code will be used for recurring payments made with a stored card must also be planned separately.



