Skip to content

Search

"card authorization"

241 articles found

Payment card being checked against a card recovery bulletin of problem cards

Merchant & POS

What Is a Card Recovery Bulletin (Card Protection Bulletin)?

A Card Recovery Bulletin is a list of problem cards (lost, stolen, expired, over-limit, counterfeit or otherwise flagged) published by card schemes such as Visa or MasterCard. It shows whether a card number is listed on the date of purchase.

Illustration explaining what a non-secure e-commerce card transaction is

Payment Systems

What is a Non-Secure transaction?

A non-secure transaction is an e-commerce transaction approved without any verification before authorization, such as SMS OTP. In short, authorization is obtained by verifying only the card number, expiration date, and CVV2.

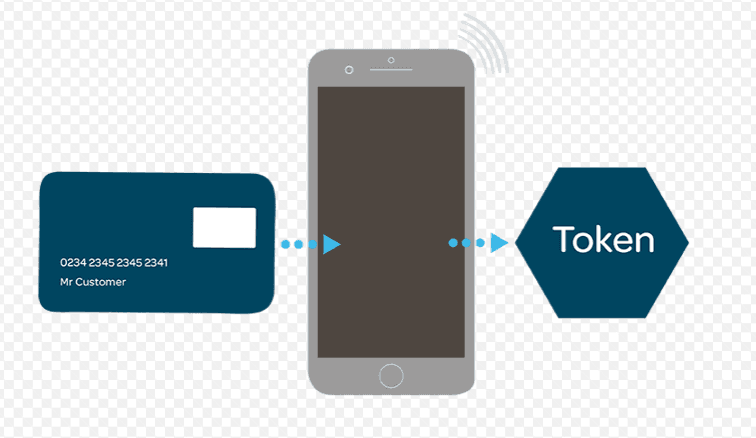
Comparison of online and offline token verification in payment transactions

HCE

What Are Transaction-Based (Online/Offline) Token Types?

Token types vary depending on the verification method used in a transaction. In offline transactions, general checks are performed by the mobile app and card reader without any verification in the card system. In online transactions, token verification is sent to and verified by the issuer.

Diagram showing an authorized card transaction that expires before reaching the clearing file

Credit Card

What does it mean for a card transaction to expire?

Due to how payment systems work, authorization is obtained for a transaction first. For a Not Onus transaction (different card and POS banks), the system waits for it to arrive via the clearing incoming file. If it does not arrive within about a week, the transaction expires.

Diagram of the online authorization flow for below-CVM-limit contactless transactions

Payment Systems

Domestic Flow Change Made for Below-CVM-Limit Online Contactless Transactions

The domestic authorization flow for below-CVM-limit online contactless transactions has changed. Issuers can now ask the cardholder for a PIN or request card insertion instead of simply approving or declining. This post explains the CVM list and the new DE48 PDS22 and DE39 = 65 message flows.

ISO 8583 field 35 Track 2 data

ISO 8583

ISO 8583 Field Descriptions (F35)

The card's Track 2 data is carried in this field. Track 2 data contains information such as the card number, expiry date and service code.

Collection POS web-based payment management dashboard

Merchant & POS

What is a Collection POS?

A Collection POS is a secure, web-based payment platform through which businesses and institutions manage their collections and generate the reports they need. Many similar products exist on the market under different names.

ISO 8583 field 19 acquiring institution country code

ISO 8583

ISO 8583 Field Descriptions (F19)

F19 — Acquiring Institution Country Code: the country to which the location of the acquiring bank's device (ATM, POS, etc.) belongs.

Illustration of personal data protection under the Turkish Personal Data Protection Law (KVKK)

Merchant & POS

What is the Personal Data Protection Law (KVKK)?

The Personal Data Protection Law was adopted by the Grand National Assembly of Turkey on 24/03/2016 and published in Official Gazette No. 29677 on 07/04/2016. It protects individuals' rights in the processing of personal data and sets the rules that data controllers must follow.

Diagram of a partial authorization where an issuer approves only part of the requested amount

Merchant & POS

What Are the Partial Authorization Requirements for an Acquirer Bank?

Partial authorization lets an issuer approve part of the requested amount when the card lacks the full balance, with the rest paid another way. This post covers the technical, receipt, clearing, reconciliation, merchant and certification requirements for acquirers.