Skip to content

Search

"card authorization"

241 articles found

Table of Visa and Mastercard fraud codes and descriptions

Security

What Are the Visa and Mastercard Fraud Codes?

Fraud means obtaining unjust gain by carrying out a transaction at a merchant or ATM using someone else's credit card or debit card, causing a loss to the real cardholder, the merchant, or the bank. So what fraud codes do Visa and Mastercard use?
Diagram of an external quarterly network vulnerability scan for PCI DSS compliance

Security

What Is a Quarterly Network Scan?

An external network scan run every 3 months by an Approved Scanning Vendor authorized by card schemes such as MasterCard and Visa, required for PCI DSS compliance. It checks whether merchant systems are protected against external threats.

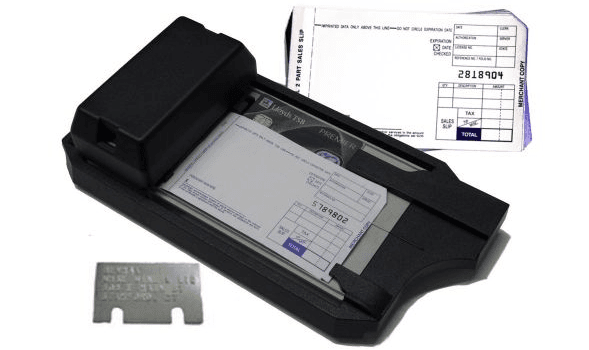
Old mechanical credit card imprinter machine used to transfer embossed card details onto a sales slip

Merchant & POS

What Is an Imprinter?

An imprinter is the name given to devices that transfer all the information embossed on a credit card onto a paper sales receipt. Before POS terminals, it was commonly used by merchants for authorization transactions.

Diagram of the EMV Card Block command process

EMV

What is the Card Block command?

The Card Block command is used after card issuance to deactivate all applications within the ICC, including applications that could be selected indirectly. The components of the command are explained below.

ISO 8583 F22 Point of Service Entry Mode table

ISO 8583

ISO 8583 Field Descriptions (F22)

F22 - POINT OF SERVICE ENTRY MODE: This field holds how the transaction was performed via the POS/ATM and the PIN entry capability of the POS device. The first 2 digits show how the transaction was performed, and the last digit (shown as x) carries the POS's PIN entry capability. Numeric...

Illustration representing the chargeback and dispute process in card payments

Chargeback

What Are the Domestic Exceptions to Chargeback Rules?

A chargeback is the refund of an amount paid by credit card to the cardholder's card when the purchased goods or services were not received, or when a transaction was not actually carried out by the cardholder.

Diagram of a first credential-on-file transaction using stored card data

Security

What is the First Credential-On-File transaction?

The first transaction made after a customer's card data is stored with a merchant is called the First Credential-On-File transaction. BKM expects it to be flagged with the value "C" in switch message field DE48.PDS86, and BRSA draft rules govern how card data may be stored.

Diagram illustrating TCR (Transaction Record Component) packets used in payment clearing and settlement files

Payment Systems

What Is TCR (Transaction Record Component)?

TCR stands for Transaction Record Component, the packets that carry transaction information in a clearing system. Transaction types in a clearing file are distinguished by transaction code and usage code values, and this data is sent inside TCR packets.

Warning illustration about a fake social media gift points scam targeting card details

Credit Card

Congratulations, You Won Gift Points..

A real attempted card fraud story: a fake Facebook friend request, a promise of free bank points, and a request for card number, expiry date and CVV2. Here is what happened and how to protect yourself.