Skip to content

Search

"Merchant Data"

96 articles found

Cover of the Visa Merchant Data Standards Manual document

Merchant & POS

What Is the “Merchant Data Standards Manual”? How Can I Access It?

Visa's Merchant Data Standards Manual covers classification, identification and data standard requirements for merchants, payment facilitators and marketplaces, including merchant naming, location and MCC rules. Here is what it contains and where to find it.
Diagram of a first credential-on-file transaction using stored card data

Security

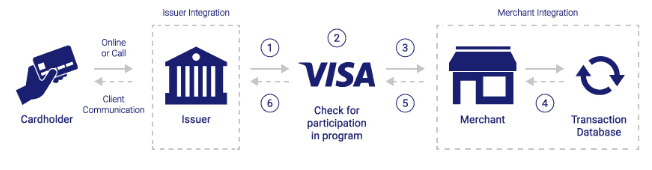
What is the First Credential-On-File transaction?

The first transaction made after a customer's card data is stored with a merchant is called the First Credential-On-File transaction. BKM expects it to be flagged with the value "C" in switch message field DE48.PDS86, and BRSA draft rules govern how card data may be stored.

Visa Merchant Purchase Inquiry (VMPI) process diagram

Fraud

What is Visa Merchant Purchase Inquiry (VMPI)?

Chargeback is the process of refunding a credit card payment when the goods or services that should have been received were not, or when transactions not made by the cardholder are identified. In Turkish it is translated as reversal of presentment.

Contactless card payment at a POS terminal with the transaction limit raised to 120 TL

Merchant & POS

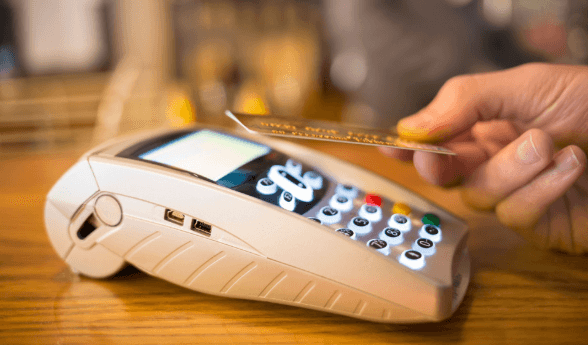
Contactless Transaction Limit Raised to 120 TL

Per BKM data, 3 in 5 merchants accept contactless payments and 1 in 10 credit card transactions is contactless. From 1 August 2019, contactless payments by card or mobile device are allowed without a PIN up to 120 TL.

Diagram showing the structure of ISO 8583 field F48 (Additional Data)

ISO 8583

ISO 8583 Field Descriptions (F48)

DE 48 - ADDITIONAL DATA: these are additional data fields that can be used specifically for transactions. It is 255 characters long. Field F48 carries many pieces of information and is divided into PDS (Private Data Subelements).

Diagram of an external quarterly network vulnerability scan for PCI DSS compliance

Security

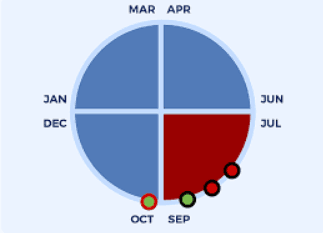
What Is a Quarterly Network Scan?

An external network scan run every 3 months by an Approved Scanning Vendor authorized by card schemes such as MasterCard and Visa, required for PCI DSS compliance. It checks whether merchant systems are protected against external threats.

POS terminal used for card payment transactions

Merchant & POS

What is On-Us Leakage?

On-Us Leakage is a term used in the world of payment systems. On-us means the card-issuing bank and the POS-acquiring bank are the same. So what does on-us leakage mean in this context?